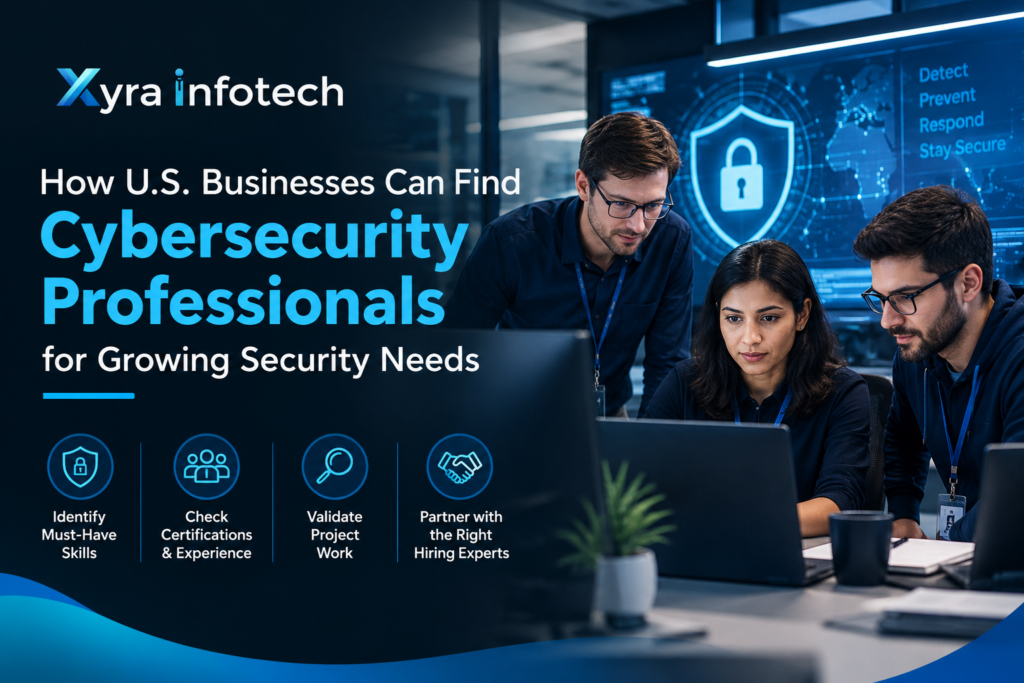
It’s possible that a growing business realizes its cybersecurity recruitment issue before it admits it. Alerts pile up. You have a security issue that goes past business hours and requires IT management to deal with it. A customer requests more controls, and it turns out no one has time to collect it. The team is working as hard as they can but have become overworked for the number of staff.
The first step towards finding the right professionals is to understand that gap. Businesses don’t need just candidates with impressive credentials, they need candidates who understand and can handle their specific risk situation, support their staff, and explain the risks clearly. For Xyra Infotech, it all begins with a question: ‘What security tasks demand improved coverage today?‘
Start With Risks, Not Job Titles
Before posting a job opening, check your technology environment and existing tasks. Pinpoint systems with sensitive information, recurring incidents, overdue improvements and tasks that rely on one overloaded employee.
The NIST’s NICE Framework offers a common terminology of describing cybersecurity activities, knowledge and abilities. It can also help employers understand what skills gaps there are in their workforce, clarify job functions and responsibilities and outline better job requirements for recruitment. It is a planning document and does not replace an awareness of their own operations.
Involve security, IT, HR and business leaders in this discussion. Decide on most important outcomes, available budget and work that will be owned by the new employee.
Matching Right people to Right Jobs
There are multiple specialties of cybersecurity. An individual who is good at spotting suspicious activity might not have a background in cloud access control or compliance documentation. Don’t hire one person to fill all jobs.
This table is a good starting point; modify responsibilities as needed to fit your environment:
| Supervisors will look for: | Discussion points with possible experts: | Evidence to Discuss |
|---|---|---|
| Answering questions about alerts | Security expert | Scheduling and documenting incidents |
| Apply access controls and conduct access configuration reviews | Protect cloud workloads | Cloud Security Engineer |
| Helping the organization get ready for audits | Governance and risk specialist | Risk assessments and control evidence |
| Security engineer | Application security engineer | Threat modelling/remediation collaboration |
These comparisons are examples only and not an all-encompassing definition of job tasks. The workload should be realistic but in smaller organizations, responsibilities may be split among the various organizations.
Job Description for the Candidate to Understand
A good posting provides information about the job and not every security product that is available. Distinguish between core skills and skills that can also be acquired on the job.
Provide relevant information for candidates:
- Systems, platforms and business operations that they will defend.
- Reporting relationships, available team support.
- Responsibilities in the event of an incident and in the event that someone is on call.
- Job site, hours, pay and employee perks.
- Top three months priorities.
Frankness with difficulties. If there is missing documentation or processes need to be built, indicate that. That opportunity may be welcomed by the right candidate – if resources and expectations are appropriate.
Seek to find New Career Paths
Think outside of traditional corporate recruiting- look to IT operators, networkers, software developers, ex-military, apprentices and internal teams. The titles they have before may be different, but their experience may still apply.
Evaluate skills that can be transferred, not looking for the same skills and qualifications in all candidates. According to ISC2 research, there are a variety of tasks that hire managers believe are appropriate for entry-level workers, including documentation, alert management, reporting and awareness training. That helps to establish realistic entry-level jobs rather than placing higher job demands on a starting salary.
Keep a number of sources. Employee recommendations, professional networks, training providers, industry conferences, or specialist recruiters can all lead to the recruitment of various candidates. Monitor if the channels are actually getting applicants that are relevant, not based on the number of applications.
Test Practical Judgment Fairly
A résumé may discuss experience, but a structured conversation will clarify application of experience. Invite candidates to discuss a previous problems, their contribution, conflicts of priority and learning.
Immediately follow with a brief exercise related to the role. Use a fictional suspicious logon, cloud permissions or flawed risk assessment for example. Inquire about what the candidate would be first to investigate and when to escalate.
Adopt the same questions and grading for every question set. Inform candidates to use tools or AI assistance or to not, safeguard their privacy, and never ask candidates for confidential information from previous employers. Ensure that assessments remain proportionate – applicants should not be required to do unpaid production work to prove competence.
Make decisions before the interviews, so that everyone is assessing the candidates according to the same expectations.
Assess Communication to Technical Skills
Security pros are dealing with individuals who don’t necessarily have a similarly technical background. They must make recommendations for practical repairs, prioritize tasks, and impart consequences.
According to ISC2’s workforce research, problem-solving, collaboration, communication, willingness to learn and strategic thinking are among the key priorities hiring managers are prioritizing. It is important that a product be technically sound, but it best complements that quality.
Have candidates describe a risk to a nontechnical manager. Listen for clarity, context and practical recommendations not for “fearful” language or jargon.
Select Recruiting Support carefully
In the competition of the top IT staffing agencies in USA, avoid those who guarantee quick placements. Inquire who performs the technical screening, what security specialties they are familiar with and how they do so to establish the relevant experience.
IT recruiting companies in USA like Xyra Infotech need to tell clients about their sourcing procedure, communication process, fees charged, replacement terms, etc. Ask employers with comparable demands for information to provide references and talk about what they do to keep information confidential.
While it is possible to find providers by searching for top IT recruiting companies in USA and best IT staffing companies in USA, these terms do not guarantee that these firms are of high quality. Reassess the genuine recruiters, their procedure and their comprehension of your world.
A helpful hiring discussion with Xyra Infotech is to think in terms of business priorities and show them the skills they need, instead of assuming that they can replace any and all security roles that come up.
Provide New Hires With Reasons to Stay
Hiring is not a solution for unclear authority, too full calendars or a lack of resources. Make sure that you have an onboarding plan in place, set up appropriate access to the organization, orient vital contacts and establish realistic goals.
Preempt frustration by discussing training, support for certifications, career development and incident coverage. Re-Orchestrate workload periodically and do not put one person in a situation of having to be the one to always take care of each urgent item.
Cyber security hiring isn’t all about having the long list of requirements. It involves clarifying the nature and purpose of worthwhile labour, providing ways and means to demonstrate capacity and shaping contexts for achievement. Believing that the answer to a crisis lies in recruitment, start there and security becomes a stronger base.
Frequently Asked Questions (FAQs)
What are the criteria for choosing a U.S. company to hire cybersecurity professionals for?
The initial step in evaluating your business’s security is to look at your team’s capacity, any outstanding projects, technology environment and security risks. They can then set the scope of work to be covered, including the investigation of alerts, protection of cloud systems, compliance or application security. The position should be reflective of those priorities and not a generic job title.
What are the skills that employers are seeking in a cybersecurity professional?
Technical skills should be evaluated in conjunction with problem solving skills, communication skills, collaborative skills and general willingness to learn within the defined context of the role within the organization. Requirements for candidates include understanding how they conduct research to identify risks; prioritize actions; record findings and make practical recommendations for improvement. It’s not about knowing all the tools you can in a job description, it’s about the right experience.
How do employers ensure that cybersecurity applicants have hands-on experience?
Structured Interviews, Reference Checks, Credential Verification and brief and focused evaluations. Technical depth can be discovered by having candidates describe their own work with respect to past projects. They can also demonstrate this fictional security area by providing a breakdown of how they analyze issues and make decisions, yet do not disclose confidential details.
How can an IT staffing agency assist companies locate Cybersecurity professionals?
IT Staffing Agencies can help with sourcing and initial screening of candidates, experience verification, interview coordination and research of the hiring market. While discussing the best IT staffing companies USA employers should inquire about their experience with cybersecurity, assessment techniques, client experiences, fees and replacement policies.
What are the strategies for keeping cybersecurity personnel once they are employed?
Businesses can best promote retention by establishing reasonable workloads, delegating responsibility, offering counseling and development opportunities and providing appropriate tools and authority. A well-structured induction, realistic targets, regular manager reviews and shared incident coverage ensure that security pro’s can add value without being overwhelmed by the entire emergency.